Osavul for Corporate Security

Protective intelligence for corporate security teams

Protective intelligence that flags risks to your people, sites and suppliers while attacks are still being planned, so your team can act first.

  • Front-Runner, Gartner Disinformation Security report
  • Deployed for NATO
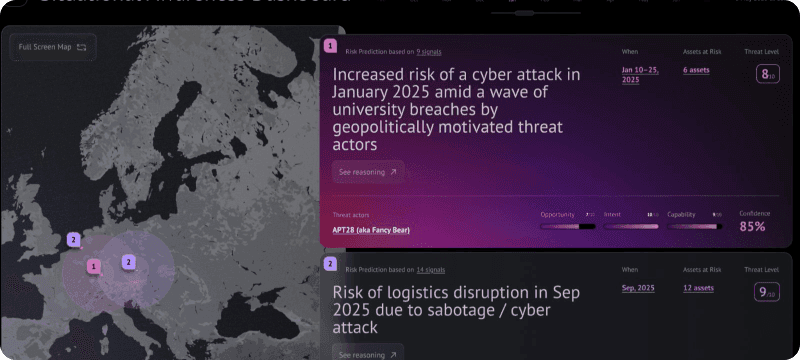
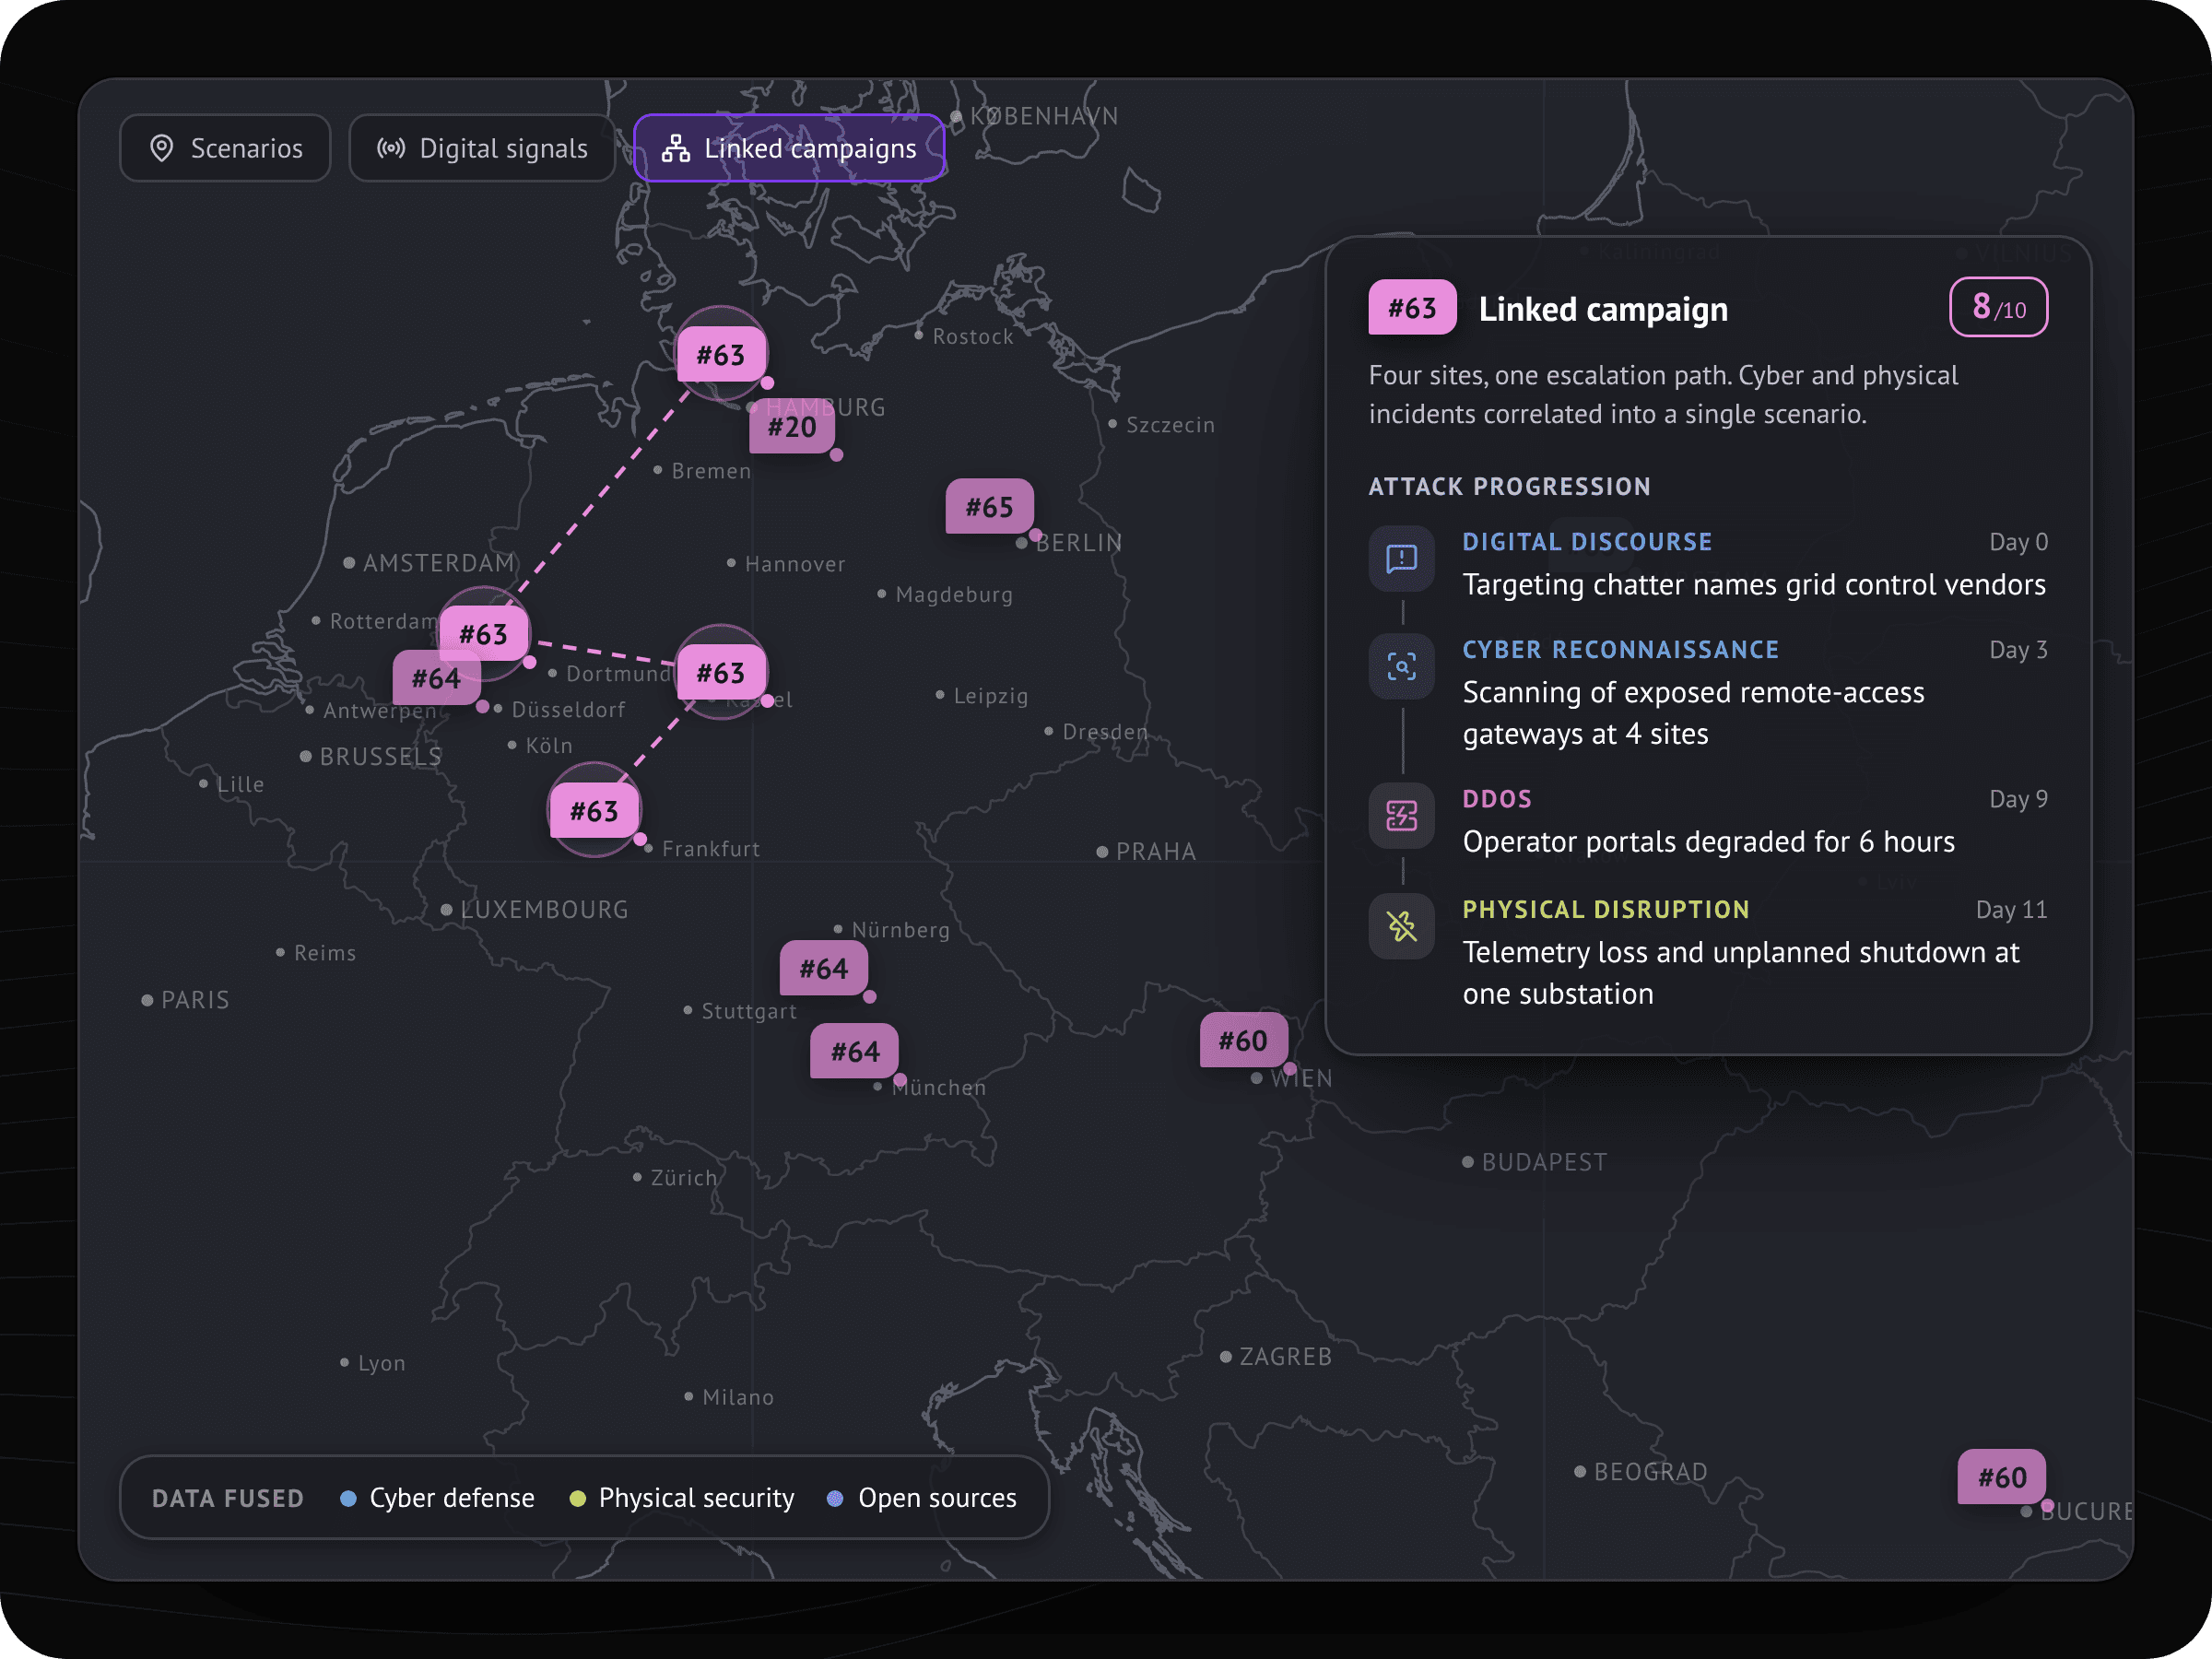
Janus map with threat alerts near company sites

Real-time alerting

Physical asset and digital signal correlation for your global security operations center

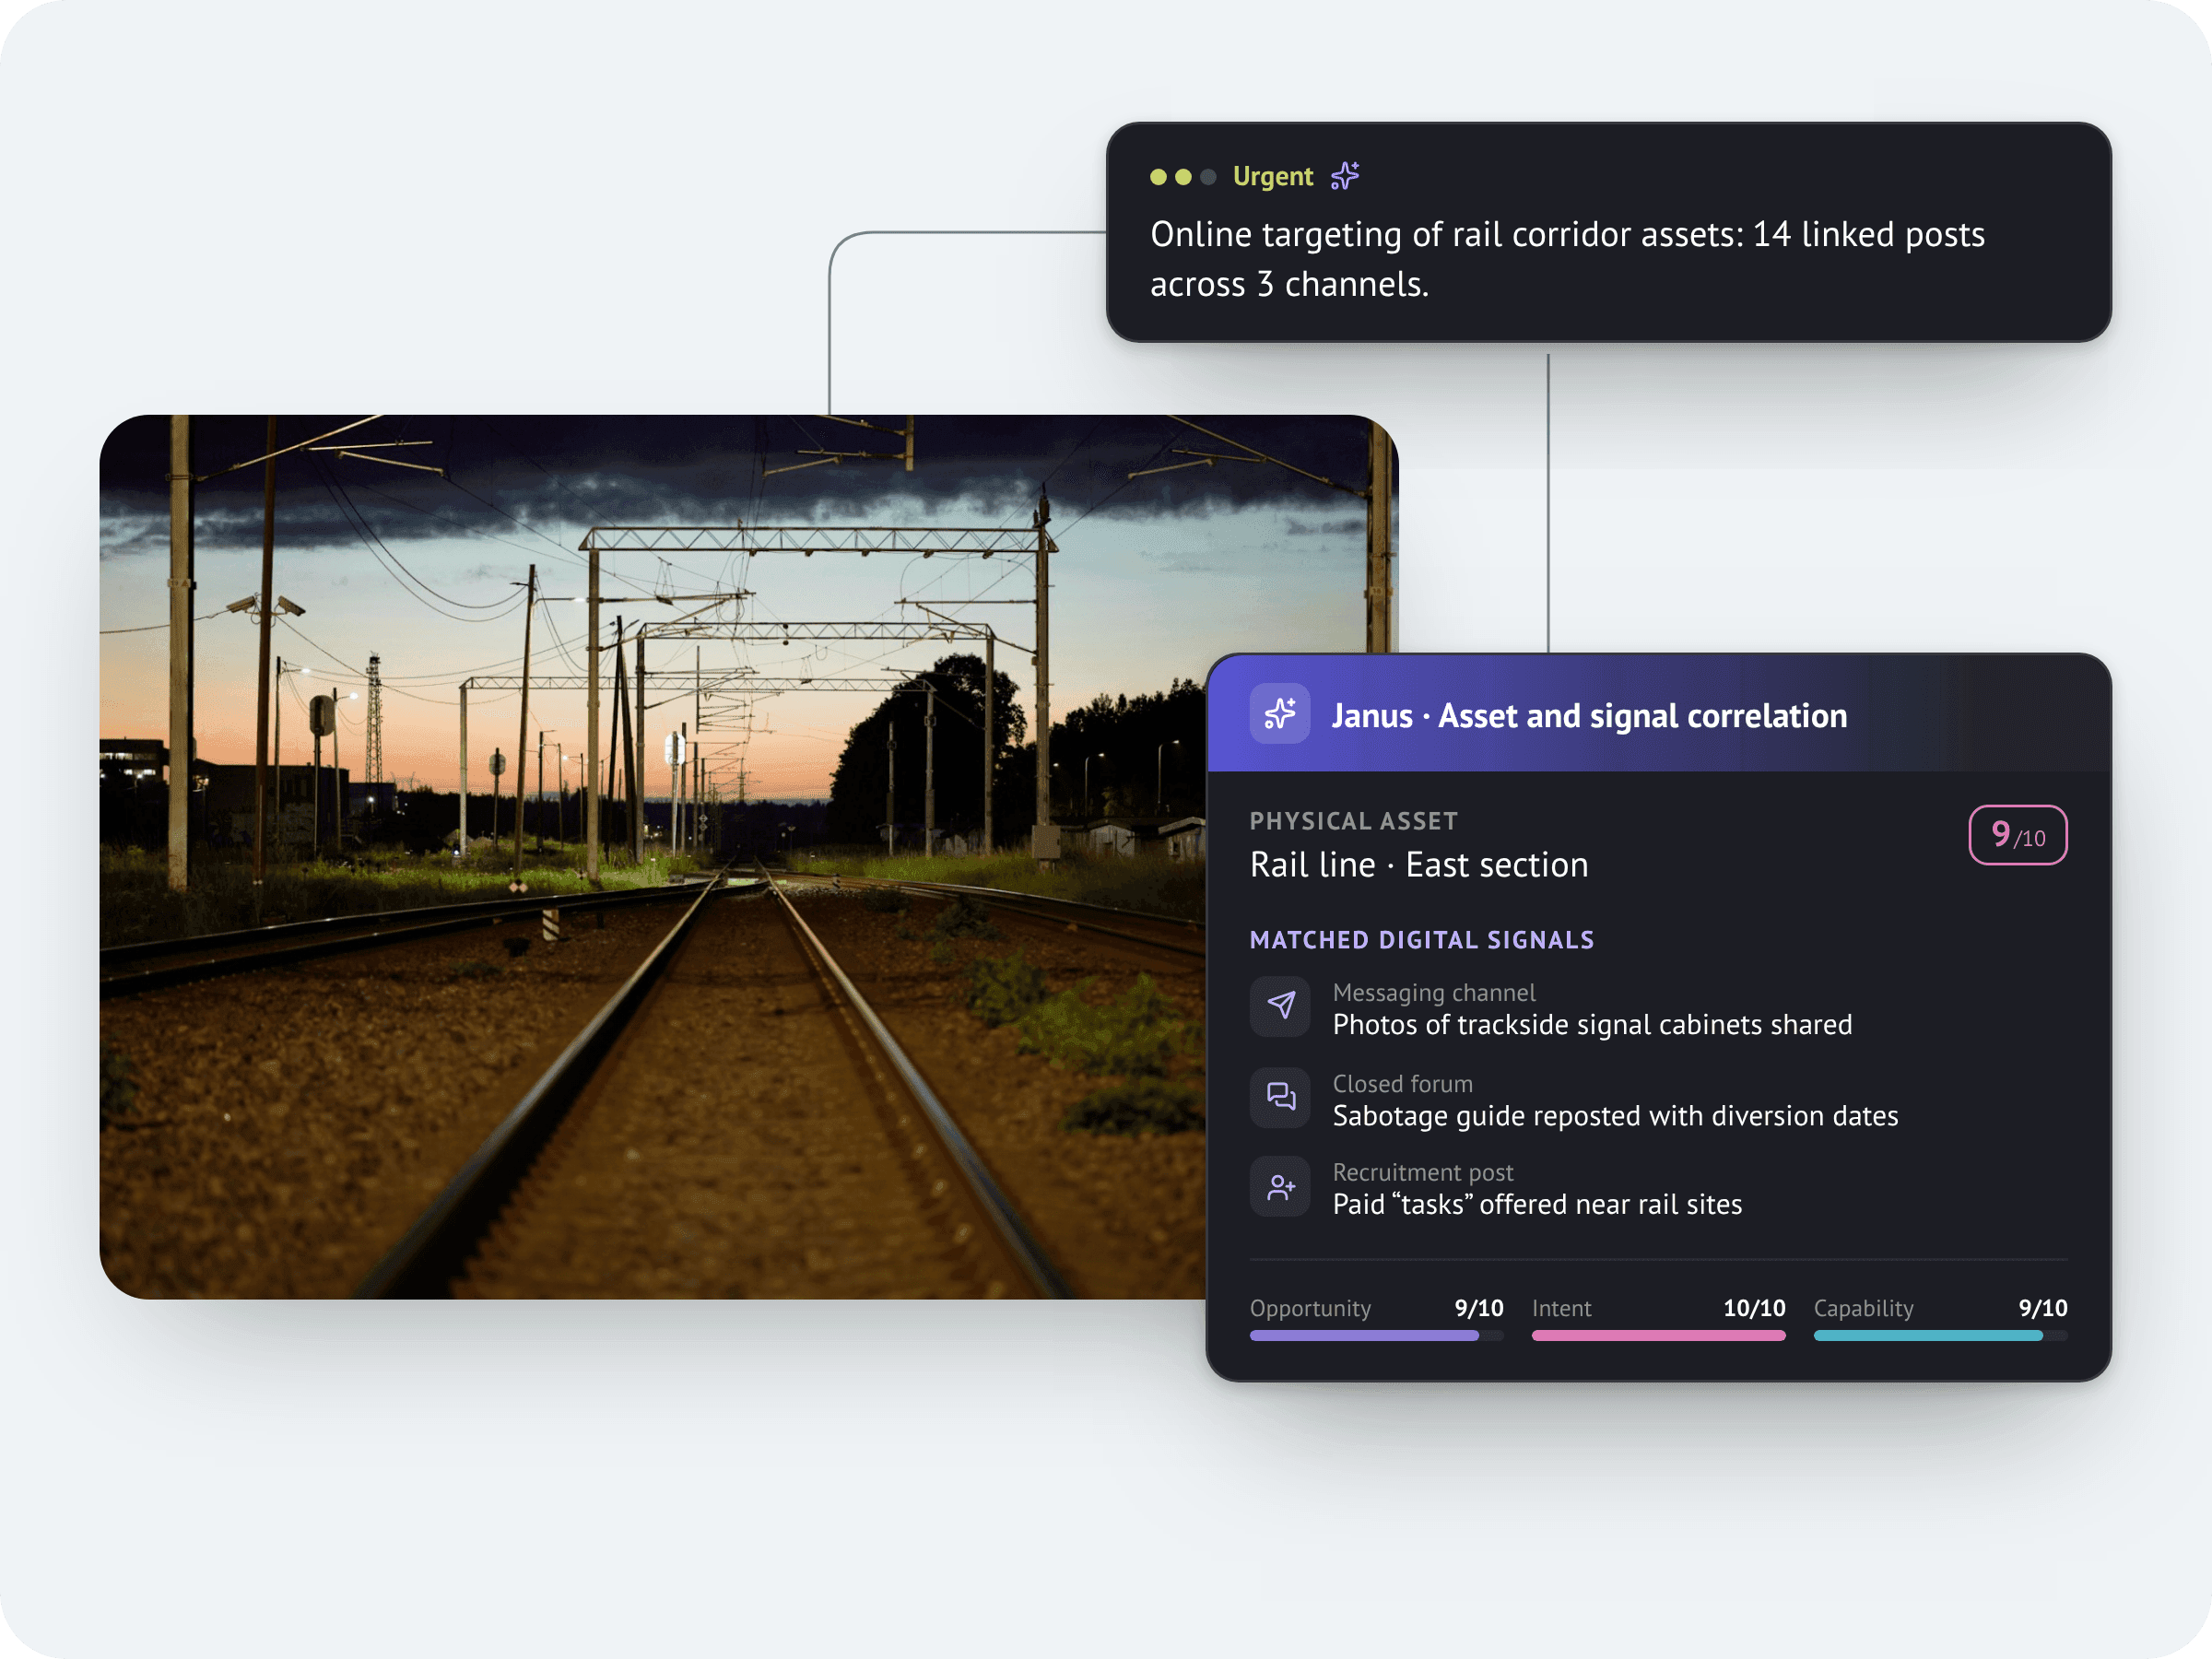
Osavul matches what it collects online against your physical asset data, so a coordinated plan to disrupt operations shows up early. It works as GSOC software and brings protective intelligence straight to your GSOC.

  • Correlates asset locations and logistics with online targeting.
  • Matches online talk against the physical weak points of your sites.
  • Real-time alerting when a new risk scenario or a new thread of discussion appears.
See it in a demo
Janus dashboard with real-time alerts for a GSOC team

AI risk modeling

Forward-looking risk scenarios from corporate security intelligence

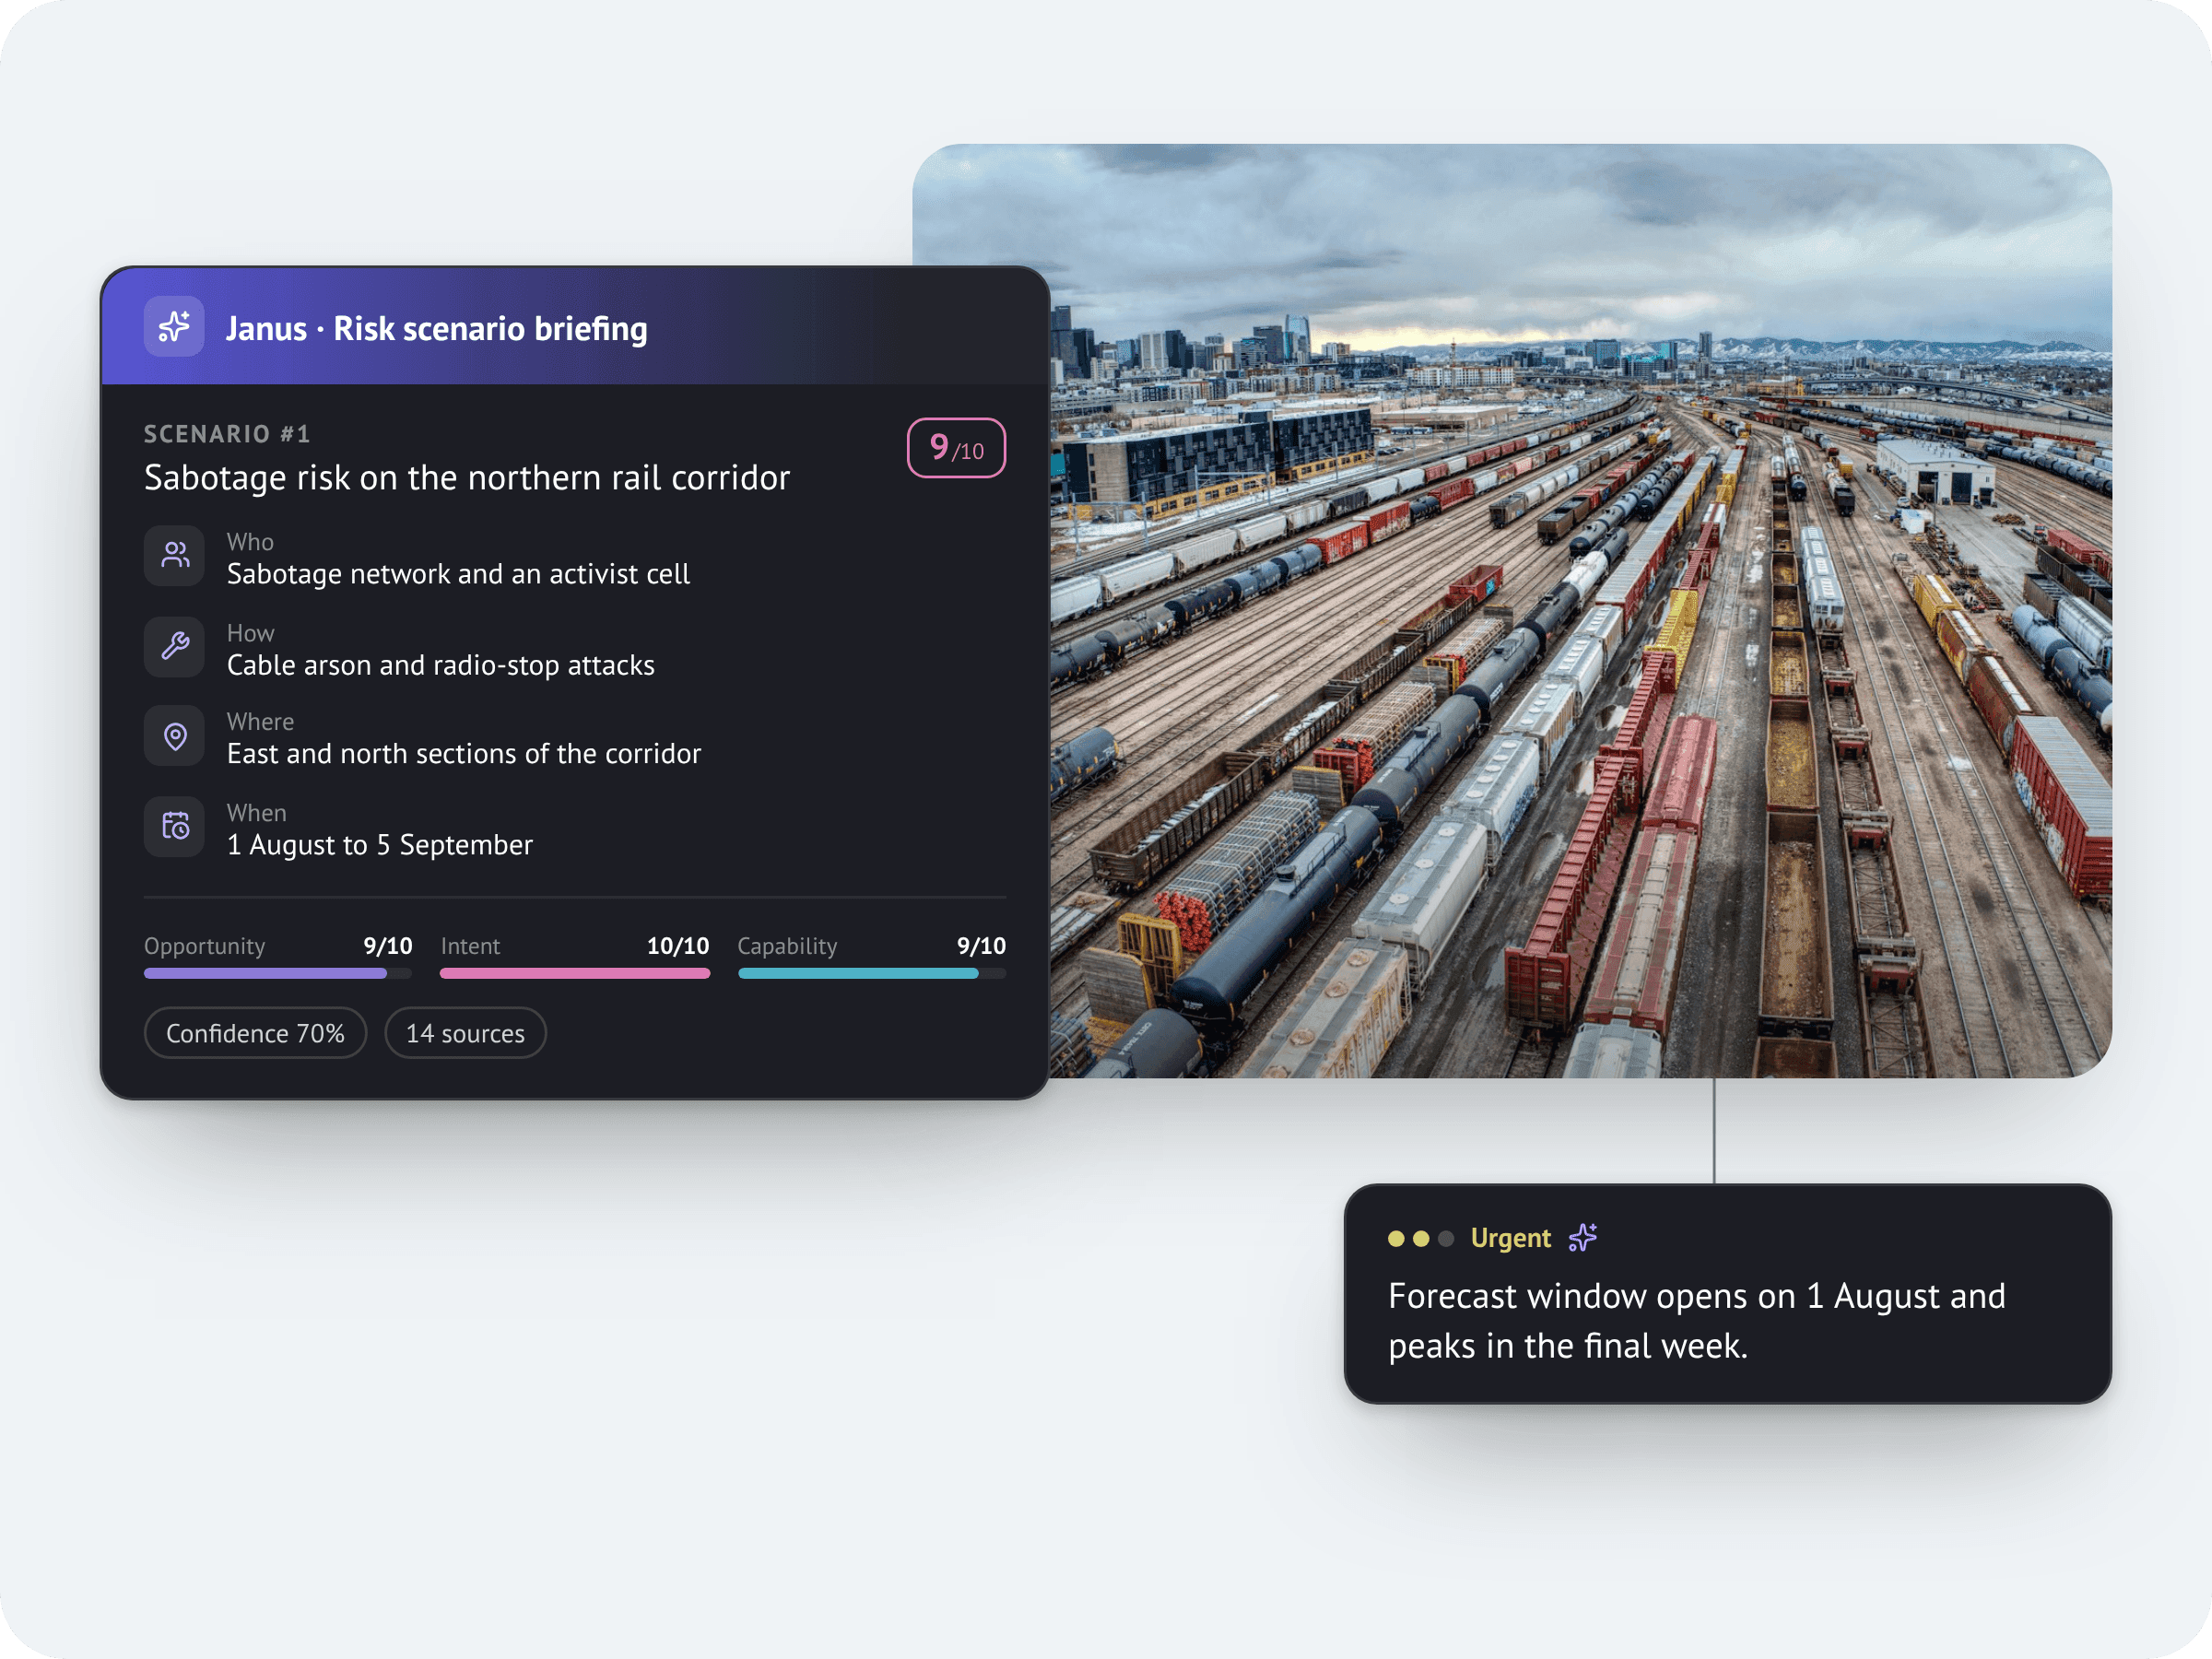
You get a structured briefing for each risk scenario: who is likely to act, how, where and when.

  • Weighs site opportunity, adversary intent and operational capability.
  • Summarizes the adversary's methods and likely targets.
  • Each scenario comes with confidence and threat level scores and an evidence chain you can audit.
See it in a demo
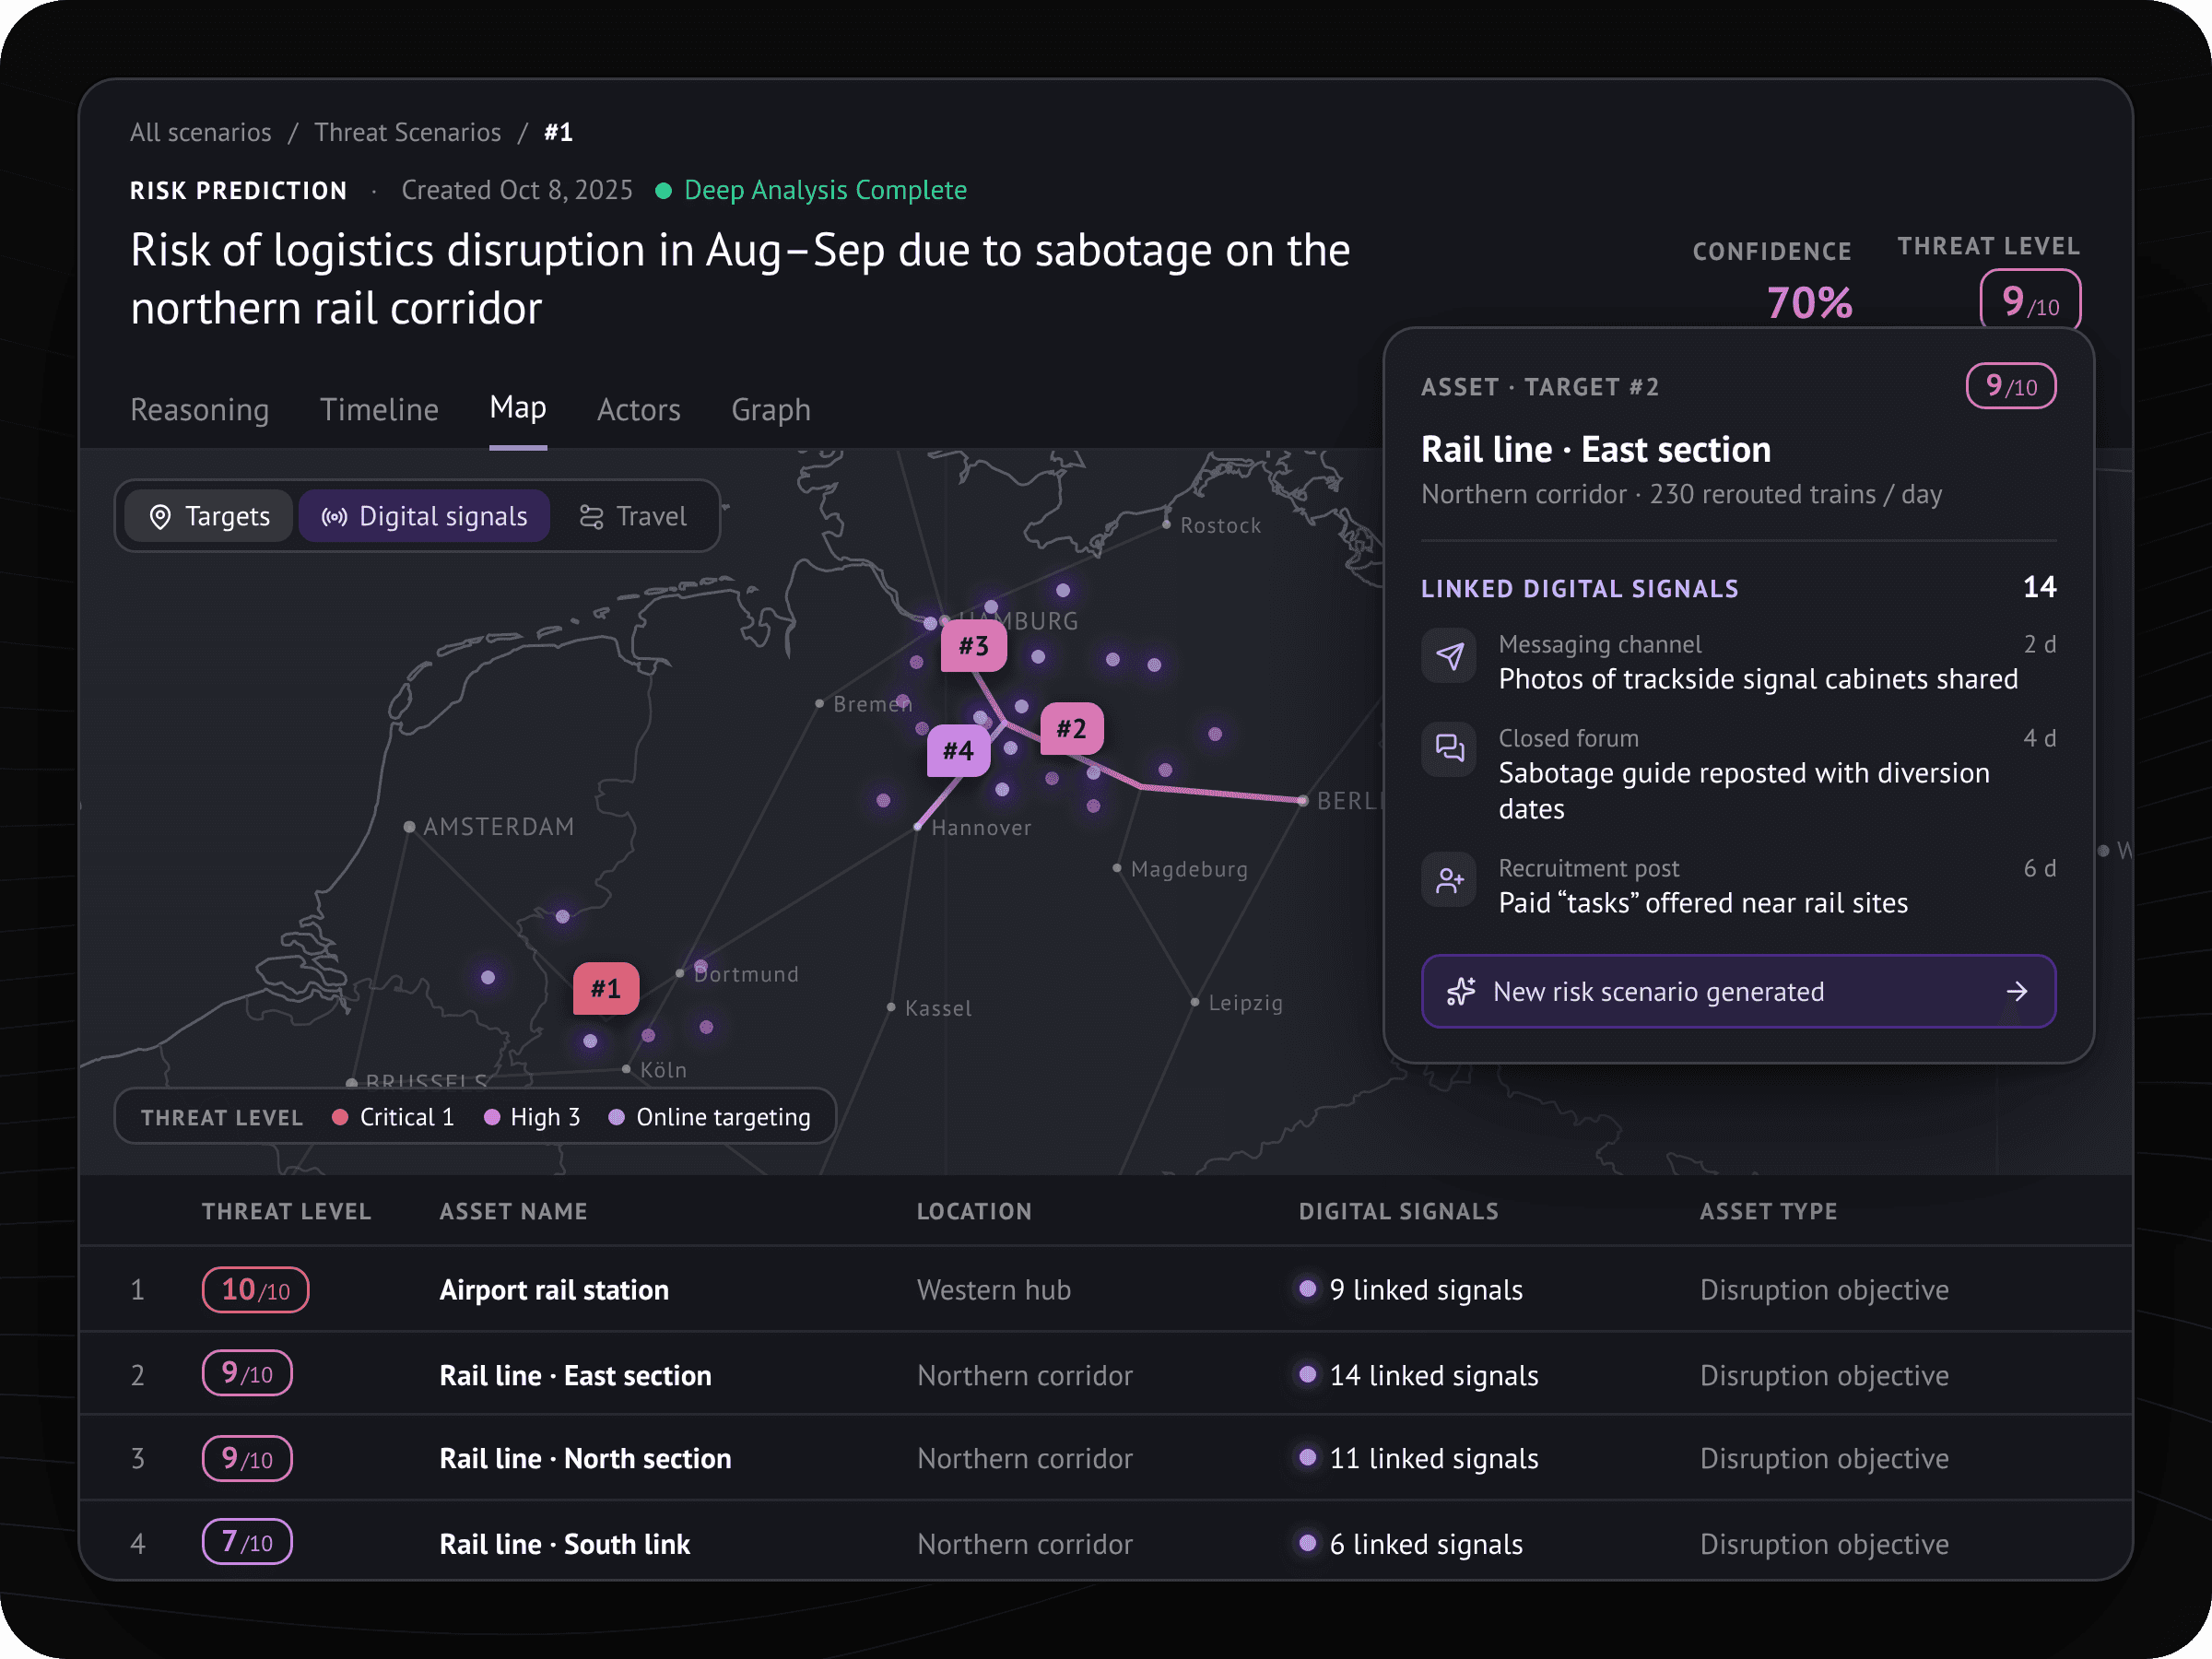
Janus forecast of a sabotage attack chain

Data visualization

Data visualization for exposure monitoring

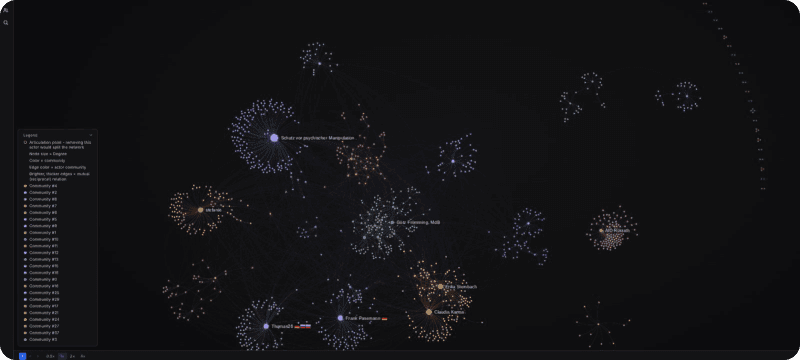
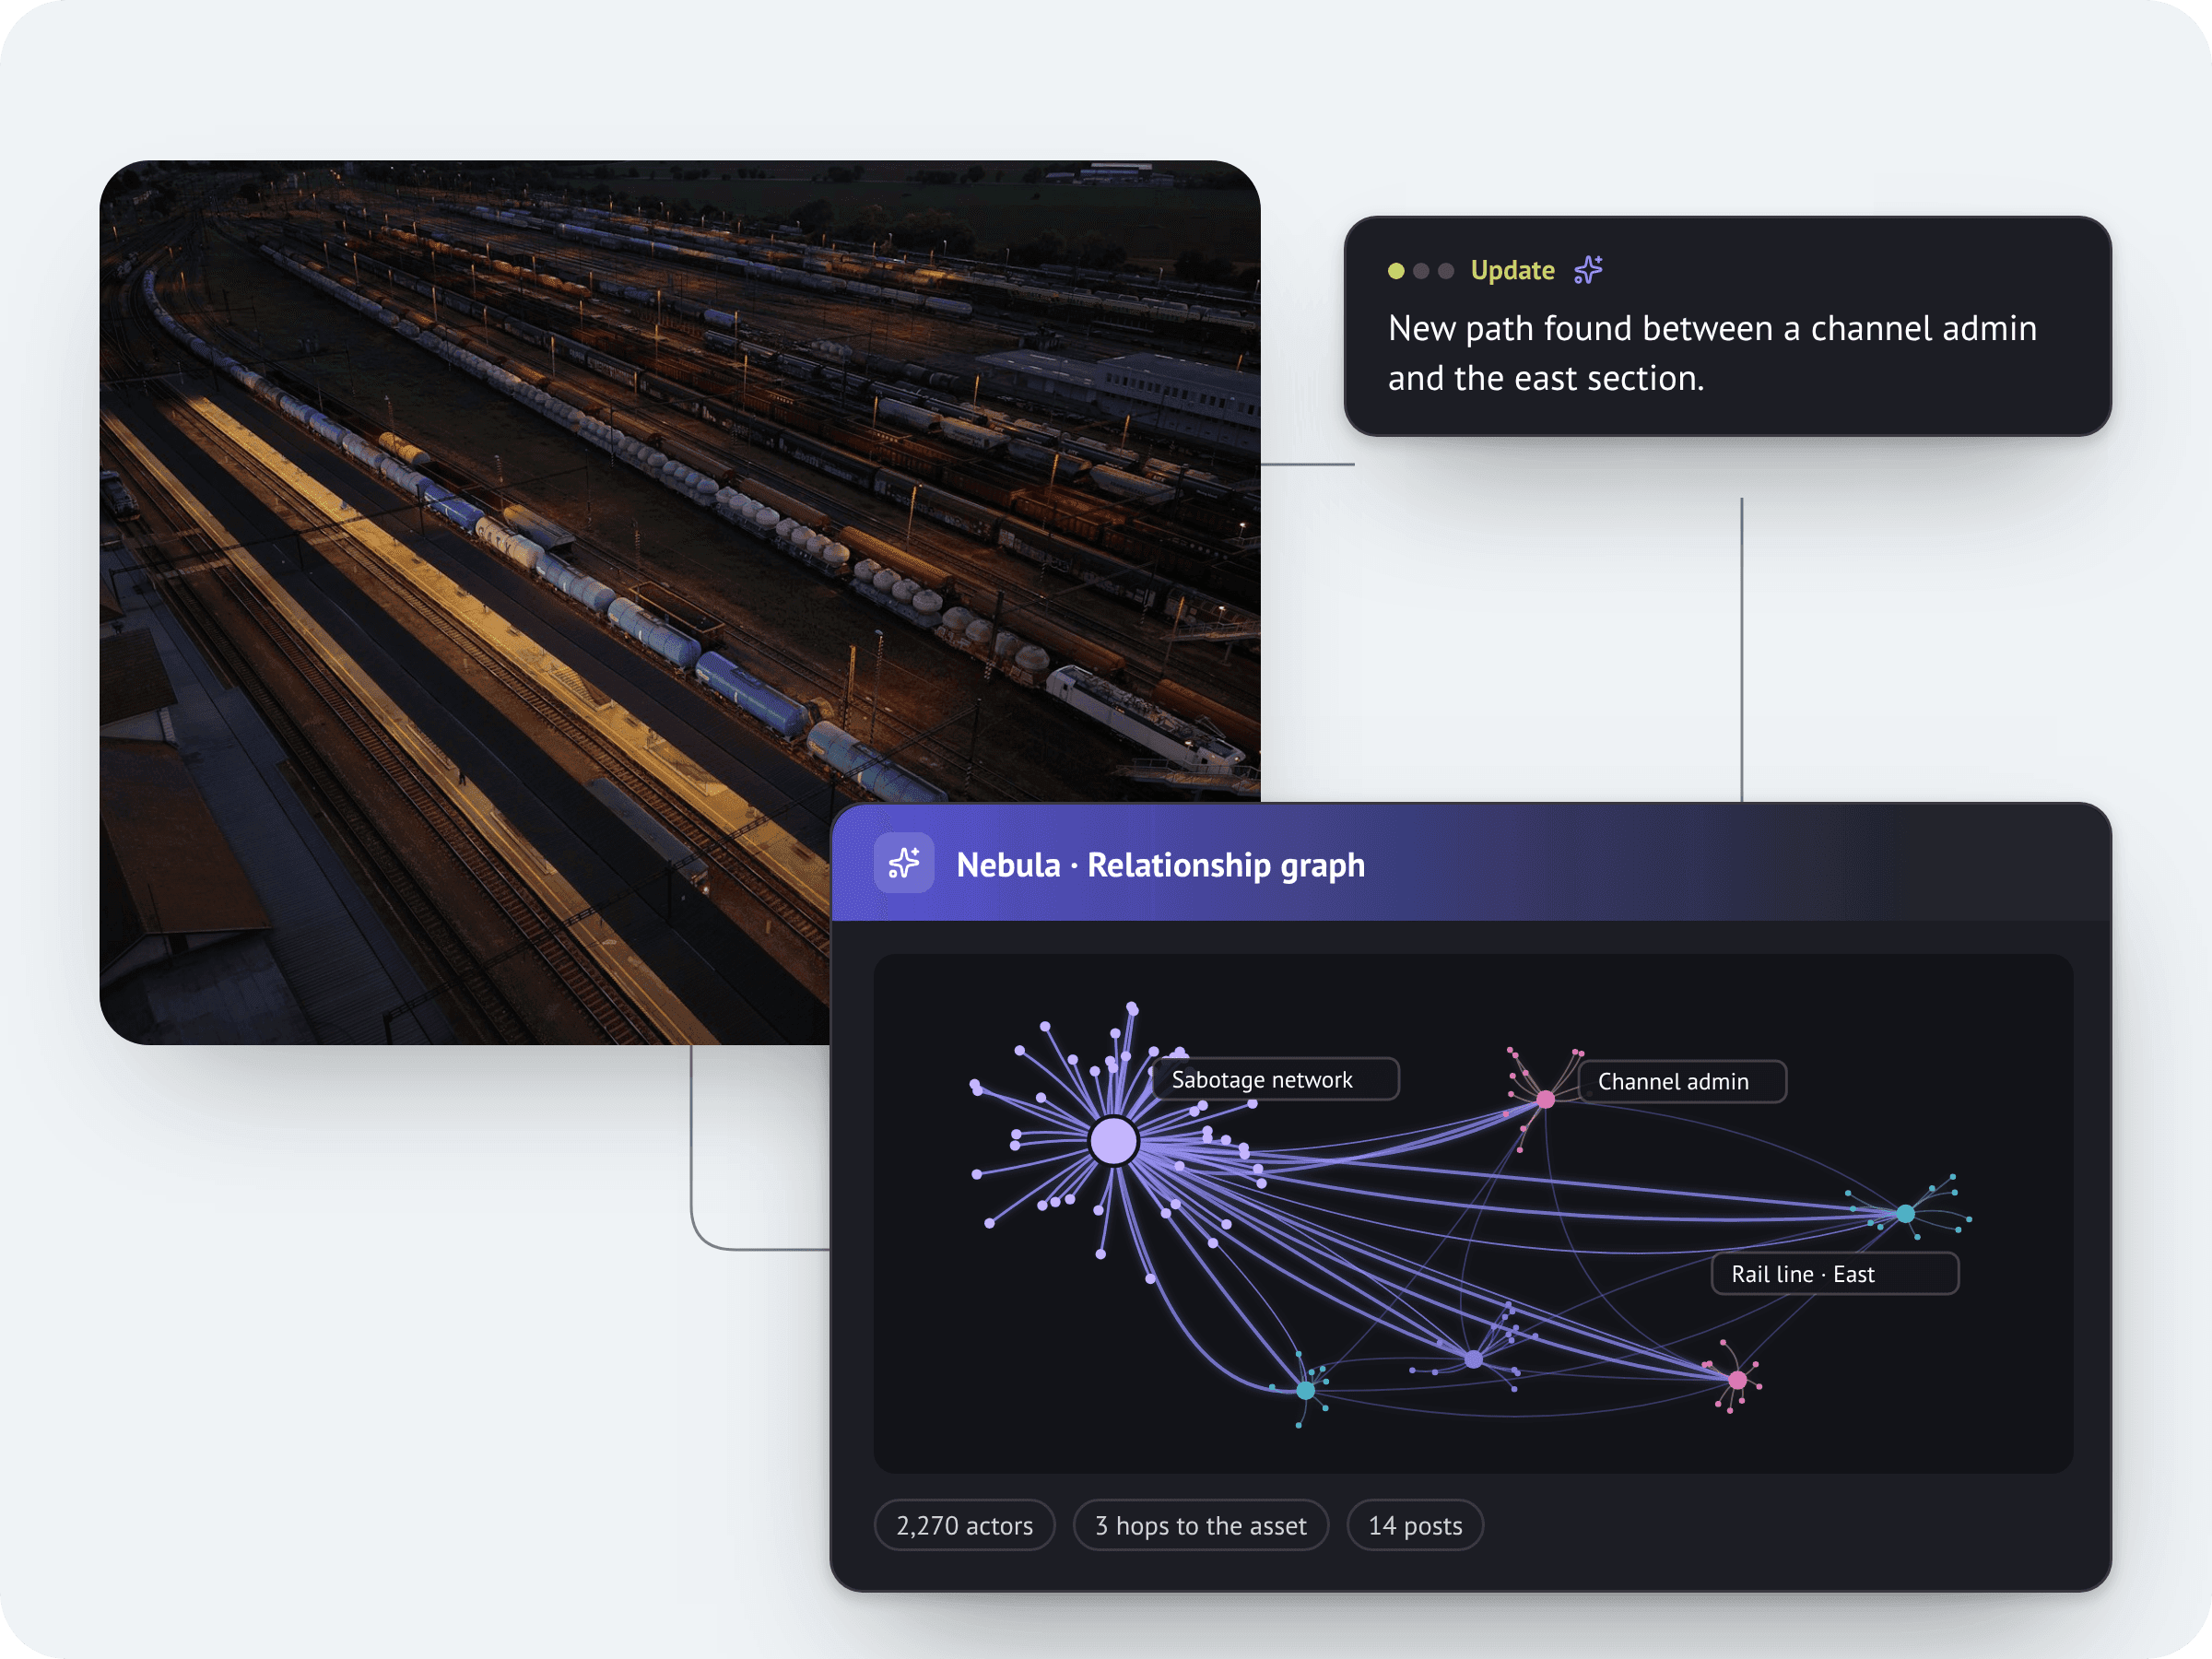
Interactive graphs show how hostile actors, tactics, accounts and physical assets connect. That includes site and executive threats that fall under your duty of care.

  • Open-source chatter, turned into network maps.
  • Links online coordination directly to physical targets.
  • Analysts get to attribution faster.
See it in a demo
Visual of data streams scanned for exposure monitoring

AI Intel Platform features

More from the protective intelligence platform

Sabotage, attacks on sites and infrastructure, surveillance and unrest near your locations and people.

Monitor underground forums, marketplaces and dark web channels for threats to your organization, people and assets.

Prioritized actions, mitigation plans, takedowns and automated defenses in your SIEM.

API and SIEM integrations, open CTI feeds, on-premise or sovereign cloud deployment.

Osavul interface: Cross-domain cyber and physical disruption correlation

We will keep working with governments and defence, where our intelligence is forged, and bring that capability to the businesses societies rely on.

Co-Founder and CEOOsavul
Janus threat forecast for a Western European national rail operator

Case study · Critical infrastructure

How a national rail operator gets early warning on sabotage risks

Challenge
Sabotage and hybrid threats against rail assets in several countries, with warning signs scattered over open, hard-to-reach and underground sources.
Solution
Janus watches stations, lines and staff and models which actors could strike, how, where and when.
Result
The security team now gets early warning and briefs leadership with assessments backed by evidence.
See the threats aimed at your people and sites

Ask us about coverage, deployment and which parts of GSOC as a service we cover, in a demo for your sector.

Book a demo
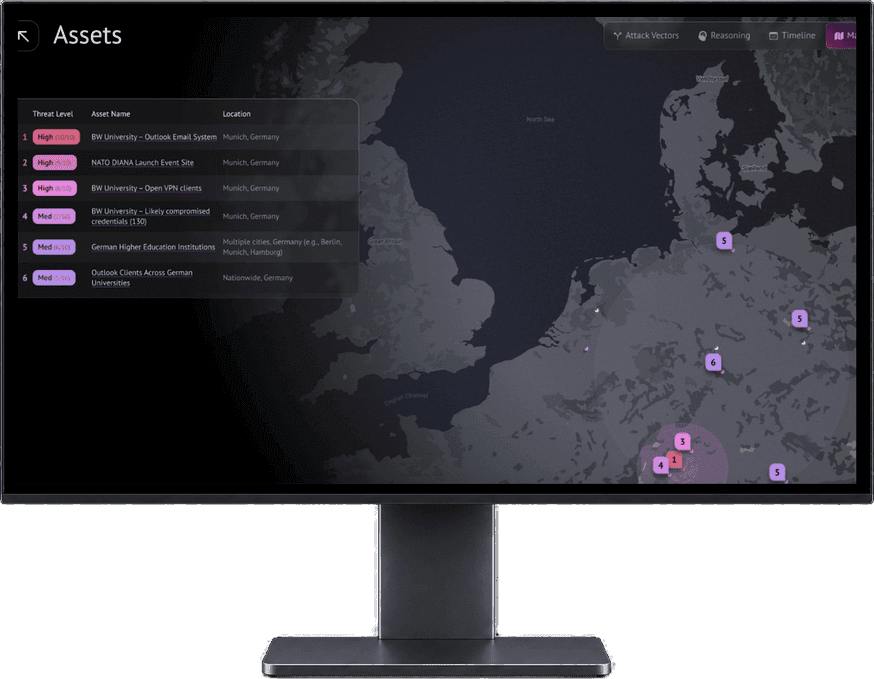
Janus risk intelligence platform on a monitor