Case study · FIMI
From Russia with Automation: how RT content gets around EU sanctions
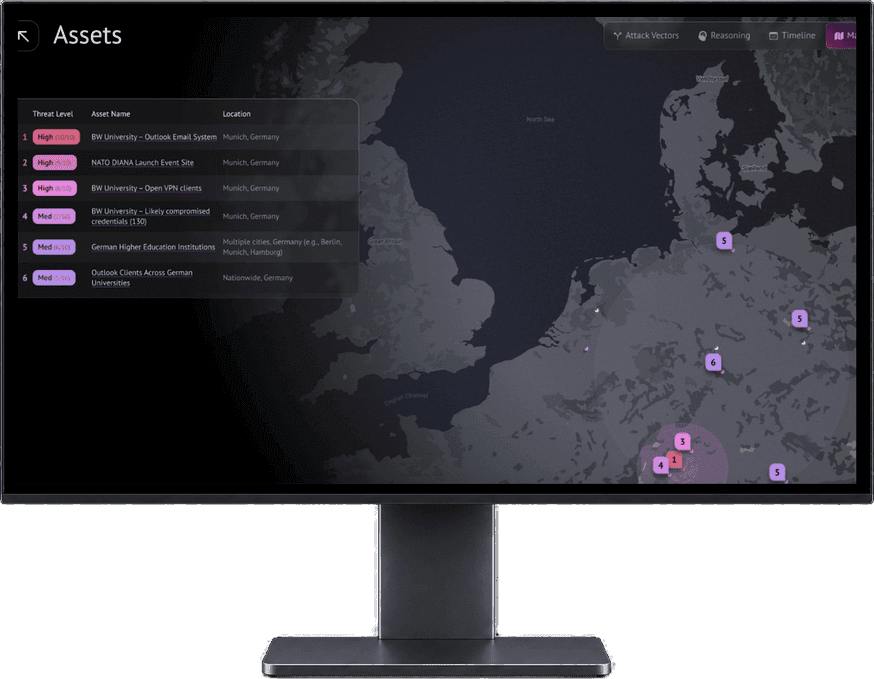
Osavul traced 33 German-language domains that keep spreading RT content in the EU despite sanctions, and the accounts amplifying it.
Read the case studyAI Intel Platform
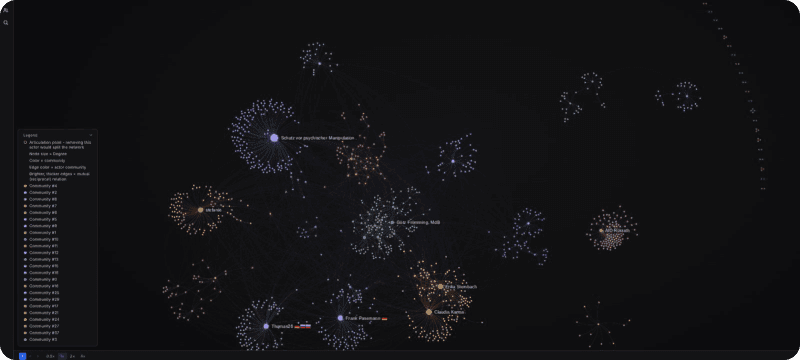 Data intelligence platformNebulaAccess and enrich data from 10+ data types, including messaging apps and underground communities, and get it in the form your analysts need.Explore Nebula
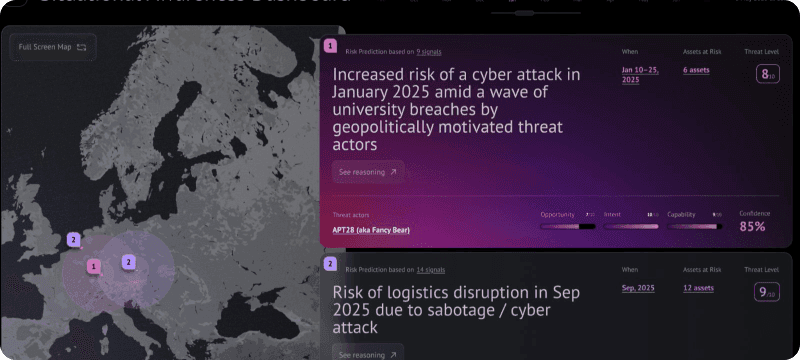 Risk intelligence platformJanusTrack physical, cyber, cognitive and hybrid threats, get early warning and model who may attack, how, where and when.Explore Janus
Products
 Osavul for Corporate SecurityDetect sabotage, espionage, and influence operations targeting your people, sites, and operations, with real-time alerts and AI risk modeling.
 Osavul for National DefenseHybrid threat intelligence and information environment assessment for defense and security institutions, from early warning to response.
 Osavul for Strategic CommunicationsDetect, analyze, and counter FIMI campaigns with narrative intelligence across social media, Telegram, and the open web in 100+ countries.
 Osavul for Brand ProtectionIdentify narrative attacks, coordinated inauthentic behavior, and reputational risks targeting your brand before they escalate.
Solutions
Find the right setup by use case, industry, or team.
By use case

Industries · Government & Public Sector
Government threat intelligence for ministries and agencies. Spot FIMI, hybrid attacks and threats to officials early, with evidence your teams can use.
Industry stats
A ministry can face a DDoS on Monday, a forged letter on Wednesday and threats against a minister by Friday. Public sector security teams rarely see those three on the same screen.
31.8%
Of the cyber incidents ENISA recorded in the EU in 2025 hit public administration, more than any other sector
82%
Of events against public administration were ideology-driven DDoS attacks
540
FIMI incidents were detected and analyzed by the EEAS in 2025
65%
Of people worry that other countries plant falsehoods in their media to deepen divisions, an all-time high
Source: 2026 Edelman Trust Barometer Global Report, January 2026
How Osavul helps
Start with the platform, or go straight to the use case your team needs to solve.
Product · Nebula
Narratives, audiences and FIMI incidents in one workspace, for ministries, strategic communications units and the people who represent governments.
Use case
A deepfake of a candidate two days before the vote is the nightmare. Osavul looks for it, and for the network ready to spread it.
Explore Election SecurityUse case
Which stories about your policies are growing, who is pushing them and which communities are listening.
Explore Narrative IntelligenceUse case
A protest heading for the ministry, a threat against a town hall, an incident at a public event: all on one live map.
Explore Situational AwarenessUse case
A cyberattack, a forged letter and a smear campaign against the same ministry are rarely a coincidence. Osavul lines them up.
Explore Hybrid Threat IntelligenceHybrid risks
Hostile actors test institutions with DDoS, leaks, forged documents and threats to officials, often in the same week. Osavul’s AI threat intelligence links each one to the campaign behind it.
State media, covert channels and inauthentic accounts push false claims about a policy, migration or aid. Osavul detects the FIMI incident and the accounts that carry it.
Learn about FIMIA group says it took down a ministry site and posts “leaked” documents. Some are real, some are forged. Osavul helps you find proof and follow the story around them.
Learn about hybrid threatsDoxxing, harassment and physical threats against ministers, civil servants and their families. Receive alerts tied to personnel and physical assets.
Learn about physical threatsCoordinated pages, fake polls and synthetic videos in the weeks before a vote. See the actors and channels well before election day.
Learn about influence operationsCooperation with NATO and the Brandwatch–Blackbird consortium represents a significant milestone for Osavul. This cooperation allows Osavul to directly support NATO’s need for timely and comprehensive situational awareness.
Case study · FIMI
Osavul traced 33 German-language domains that keep spreading RT content in the EU despite sanctions, and the accounts amplifying it.
Read the case studyFAQ
Threat and narrative intelligence for ministries, agencies and public bodies.
Talk to a threat analystGovernment threat intelligence is knowing who is going after your institution, your officials and your citizens, and how they plan to do it. Cyber is one part. A forged decree on Telegram or a man photographing a minister’s house is another. The earlier you see the pattern, the smaller the fire.
Most ministries already run social listening for the press office, and that’s a good start. For threats you need Telegram and emerging platforms too, a way to spot accounts acting in concert, and an alert when someone names an official. Osavul adds that, and comms, crisis and security people all get the same findings.
Osavul gives counter-FIMI units one place to work. Log an incident, keep the evidence, map who and what was involved, then watch the same TTPs come back months later. Because every case is written up separately, you can hand it to EU or NATO partners, or use it in your crisis communication, the same day.
Osavul is a Luxembourg company and handles data under the GDPR. If your rules say the data stays in the building, it stays there; if a sovereign cloud is allowed, Osavul uses that. Access is role-based and every action is logged, which helps with NIS2. Certifications and procurement paperwork get settled during scoping. [TO CONFIRM with Legal and Product: certifications]
It should pull from open, social and messaging sources, make sense of narratives, actors and threats, keep an audit trail anyone can check, and stay under national control. In Osavul, Nebula handles the data and narrative side and Janus adds hybrid risk modeling. You get both in one setup.
Book a demo built around your mandate, people and sites.
Book a demo