Case study · Espionage
How Osavul spotted a LinkedIn espionage campaign against NATO before it took shape
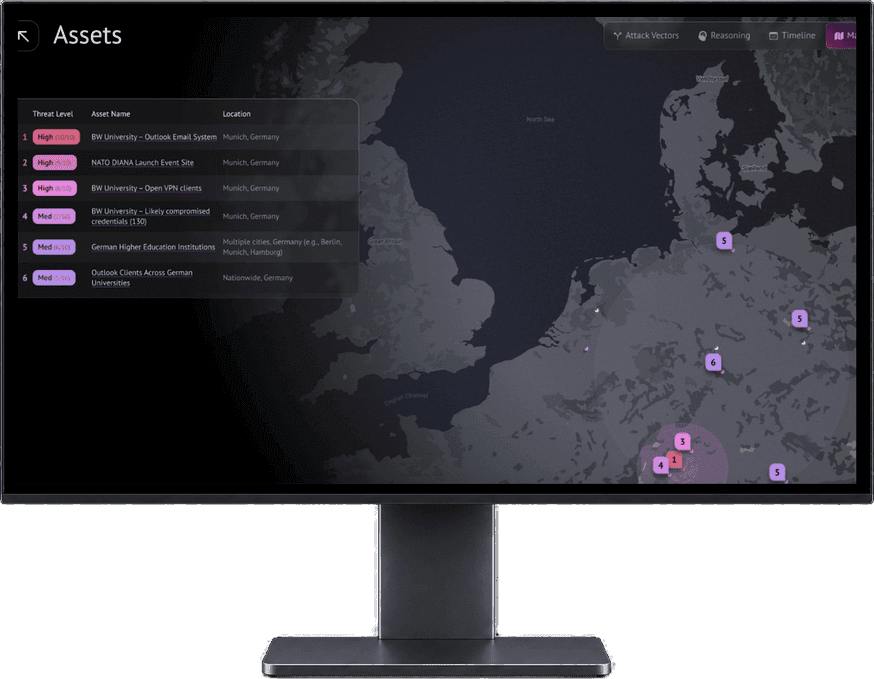
Janus modeled a LinkedIn recruitment campaign against NATO and EU officials two months before it was made public.
Read the case studyAI Intel Platform
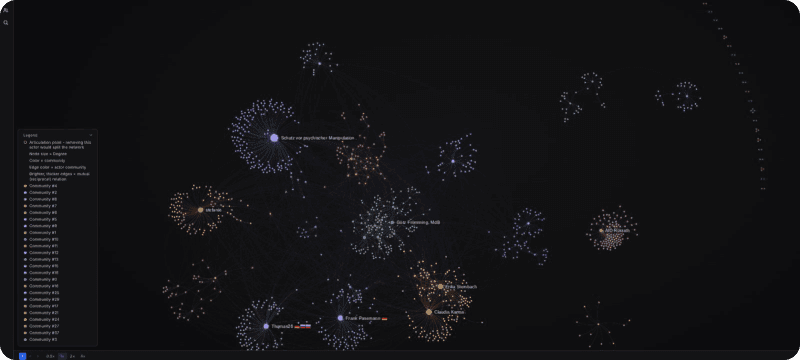 Data intelligence platformNebulaAccess and enrich data from 10+ data types, including messaging apps and underground communities, and get it in the form your analysts need.Explore Nebula
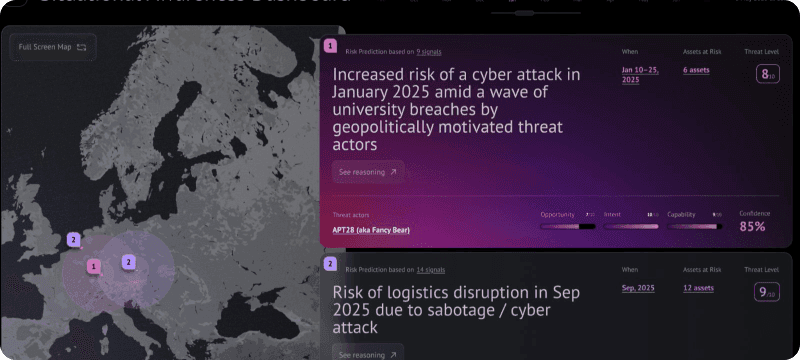 Risk intelligence platformJanusTrack physical, cyber, cognitive and hybrid threats, get early warning and model who may attack, how, where and when.Explore Janus
Products
 Osavul for Corporate SecurityDetect sabotage, espionage, and influence operations targeting your people, sites, and operations, with real-time alerts and AI risk modeling.
 Osavul for National DefenseHybrid threat intelligence and information environment assessment for defense and security institutions, from early warning to response.
 Osavul for Strategic CommunicationsDetect, analyze, and counter FIMI campaigns with narrative intelligence across social media, Telegram, and the open web in 100+ countries.
 Osavul for Brand ProtectionIdentify narrative attacks, coordinated inauthentic behavior, and reputational risks targeting your brand before they escalate.
Solutions
Find the right setup by use case, industry, or team.
By use case

Industries · Defense Industry & Manufacturing
Early warning on industrial espionage, arson and insider recruitment aimed at defense manufacturers, their plants, their people and their suppliers.
Industry stats
More shells and drones are built in Europe for Ukraine every month. The plants that make them notice who else is watching: a man filming the gate, a recruiter writing to an engineer, a fire nobody can explain.
321
Suspected cases of sabotage in Germany in 2025, by the federal police count
Source: BKA report cited by NDR and WDR, via Euronews, April 2026
10+
Military-industrial sites in Europe faced sabotage or reconnaissance attempts in August 2026 alone
21
European companies appeared on a Russian defense ministry list of drone suppliers to Ukraine in April 2026
Source: BfV, Security Notice for Business 02/2026, July 2026
6.9%
Of the cyber incidents ENISA recorded in the EU in 2025 hit manufacturing
How Osavul helps
Start with the platform, or go straight to the use case your team needs to solve.
Product · Janus
Protective intelligence for the people who secure plants, test ranges, executives and suppliers. Alerts as things happen, profiles of the actors and a forecast of their next move.
Use case
When someone probes your network and photographs your plant in the same week, you see it as one story.
Explore Hybrid Threat IntelligenceUse case
Find out early when executives are being followed, doxxed or named as targets.
Explore Executive ProtectionUse case
Which plant or supplier is likely to be hit next, by whom and how. Act on it before it happens.
Explore Risk Modeling & Early WarningUse case
Who is the recruiter, which company does he claim to work for, and who else has he written to? Find out.
Explore OSINT InvestigationsHybrid risks
Hostile services don’t pick one tool. They hire a proxy, probe your network and message your staff at the same time. Osavul’s AI threat intelligence connects those moves for your plants, people and suppliers.
An engineer gets a friendly message from a headhunter who doesn’t exist. Osavul spots the approach, the fake profile and the staff data that made your engineer easy to find.
Learn about espionageProxies hired on Telegram film a site, then come back with a fire starter. Osavul picks up the job post, the target list and the photos before the second visit.
Learn about sabotageA small supplier with weak security can stop your line as surely as an attack on your own plant. Osavul watches the companies your production depends on.
Learn about hybrid threatsYour plant’s address shows up in a post calling it a legitimate target. Hacktivists repeat it. Osavul sees that thread before anyone turns up.
Learn about narrative attacksWe will keep working with governments and defence, where our intelligence is forged, and bring that capability to the businesses societies rely on.
Case study · Espionage
Janus modeled a LinkedIn recruitment campaign against NATO and EU officials two months before it was made public.
Read the case studyFAQ
Hybrid risk intelligence for defense manufacturers and their suppliers.
Talk to a threat analystIt’s the theft of trade secrets, designs or production data for a competitor or a foreign intelligence service. Industrial espionage in defense rarely starts with a break-in. More often it’s a LinkedIn message to an employee, a supplier with poor security or someone quietly inside the network, and sometimes it’s the scouting before sabotage.
Defense manufacturers deal with recruitment of insiders, intrusions, arson and explosives at plants, drones over sites and threats to executives. German security services warned in 2026 that firms supplying Ukraine are likely targets. Osavul tracks all of it and adds the context that defense industrial base cybersecurity tools leave out.
Start with people, not software. Agree with HR, security and IT which roles matter most, teach staff to report strange approaches and check what employees give away online. That’s basic manufacturing security. An insider threat program then needs an outside view as well, and Osavul provides it through corporate espionage monitoring.
You add your key suppliers and subcontractors to the assets Osavul watches. Janus then flags breaches, sabotage, recruitment of their staff and campaigns that could stop your production, and ranks each risk by likely impact. Your team sees supplier risk next to threats to your own sites, not in a separate report.
Yes. Some Osavul clients keep everything on their own servers, others use a sovereign cloud. Either way, data about your sites, people and incidents doesn’t leave your jurisdiction. Before anything is collected, Osavul solution architects sit down with your security and IT people to agree the setup, the integrations and who gets access.
Book a demo built around your sites, programs and suppliers.
Book a demo